Managing Authentication Tokens
The Posit Package Manager Authentication Tokens page provides a web interface to create, view, filter, and revoke API tokens. This complements the CLI-based token management commands described in Token Authentication.
Accessing Token Management
The first global:admin token must be created using the CLI. Once you have an admin token, you can use the web interface to create additional tokens. See Token Authentication for CLI instructions.
To access the Authentication Tokens page:
- Sign in to Package Manager with a token that has
global:adminscope - Open the user menu in the top-right corner of the navigation bar and select Settings
- Select Token Management from the sidebar
Creating Tokens
To create a token:
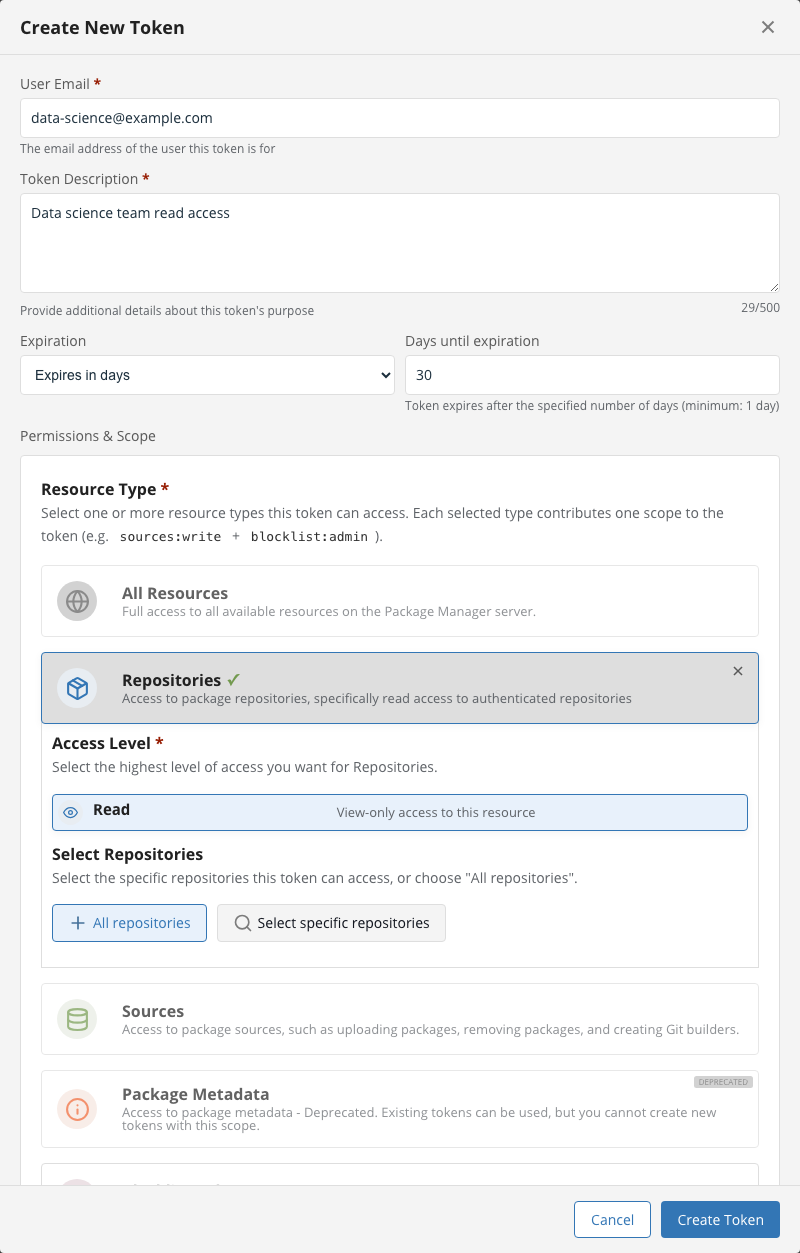
- Select the Create Token button
- Fill in the required fields:
- User Email - Email address of the user this token is for
- Token Description - Clear description of the token’s purpose (max 500 characters)
- Permissions & Scope - Select one or more resource types and an access level for each
- Configure expiration
- Select Create Token
- Copy the token immediately - it won’t be shown again
The token value is only displayed once at creation time. If you lose it, you must create a new token.
EnhancedAdvanced If you enable package requests, Package Manager sends package request email notifications to User Email. See Changing a token’s email.
Permission Scopes
Each resource type and access level that you select adds one scope to the token. Select more than one resource type to give a single token several scopes, such as Sources and Git Credentials for a Git builder.
See API Token Scopes for what each scope grants and for the scopes in each license tier.
Expiration Options
You can set when a token expires:
- Never expires - Token remains valid indefinitely (use for service accounts)
- Expires in days - Token expires after specified number of days (recommended: 30-90 days)
- Expires on date - Token expires on a specific date
For security, set expiration dates on tokens whenever possible and rotate tokens regularly.
Resource Selection
For Repositories and Sources scopes, you can choose:
- All Resources - Access to all current and future resources (use
*) - Specific Resources - Access limited to selected repositories or sources
When a token is created for a specific source or repository, deleting and recreating that resource will require a new token.
Viewing Tokens
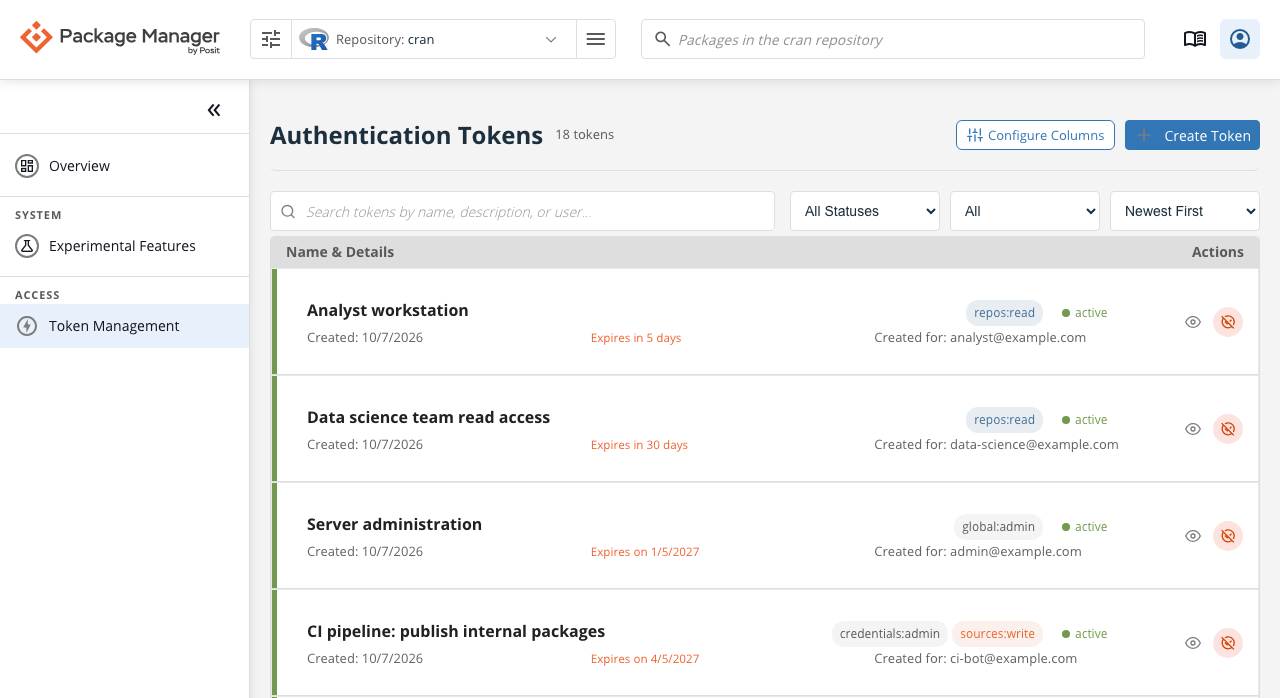
The token list displays:
- Status indicator - Color-coded dot (green=active, gray=revoked, red=expired)
- Token name/description - Primary identifier
- Status badge - Active, Revoked, or Expired
- Scope badge - Permission level
- Creation date - When the token was created
- Expiration date - When the token expires or “Never expires”
- User - Email address associated with the token
Select any token row to view detailed information including the token ID, full description, scope details, and usage information.
Customizing Columns
To customize visible columns:
- Select Configure Columns near the top-right
- Select or clear columns to show or hide:
- Token Name
- Token ID
- Status
- Scope
- Created Date
- Expiration Date
- Created For (User)
Your preferences are saved in the browser.
Filtering and Searching
Use the search bar to find tokens by name, description, or user email. The search is case-insensitive.
Status Filter
Filter tokens by status:
- All Statuses - Show all tokens
- Active - Show only tokens that can currently be used
- Revoked - Show only tokens that have been revoked
- Expired - Show only tokens past their expiration date
Expiration Filter
Filter tokens by expiration:
- All - Show all tokens regardless of expiration
- Never Expires - Show only tokens without an expiration date
- Has Expiration - Show only tokens with a future expiration date
- Expired - Show only tokens that have expired
Sorting
Sort tokens using the Sort By dropdown:
- Newest First - Recently created tokens first (default)
- Oldest First - Oldest tokens first
- Name (A-Z) - Alphabetical by token description
- Name (Z-A) - Reverse alphabetical
Active tokens always appear before revoked or expired tokens.
Revoking Tokens
Revoke tokens when they’re no longer needed or if compromised.
To revoke a token:
- Find the token in the list
- Select the Revoke button (trash icon) in the actions column
- Confirm the revocation
- The token is immediately revoked
You can also revoke from the token details modal by selecting Revoke Token at the bottom.
Revocation is immediate and permanent. Revoked tokens cannot be reinstated. You must create a new token to restore access.
Common Workflows
Creating a Repository Read Token
For users who need to download packages:
- Select Create Token
- User Email:
analyst@example.com - Description:
Read access for data science repositories - Permissions:
- Resource Type: Repositories
- Access Level: Read
- Resources: Select specific repositories or All repositories
- Expiration:
Expires in 90 days - Select Create Token and copy the value
Creating a Sources Upload Token
Advanced
For package maintainers who upload to specific sources:
- Select Create Token
- User Email:
maintainer@example.com - Description:
Upload packages to internal-python source - Permissions:
- Resource Type: Sources
- Access Level: Write
- Resources: Select specific source
- Expiration:
Expires in 365 daysorNever expires - Select Create Token and share securely
Rotating Tokens
To rotate an existing token:
- Filter or search to find the old token
- Create a new token with the same permissions
- Update all systems to use the new token
- Test that the new token works
- Revoke the old token
Auditing Tokens
To review token usage:
- Sort by Oldest First
- Filter to Active status
- Review tokens without expiration dates
- Revoke unused or unnecessary tokens
- Create new tokens with expiration dates as needed
Troubleshooting
Token Creation Fails
If token creation fails:
- Check all required fields are filled correctly
- Verify email format is valid
- Ensure description is under 500 characters
- Check that you’ve selected both resource type and access level
- Check browser console for specific error messages
Token Not Visible After Creation
If a created token doesn’t appear:
Clear all filters (select the Clear filters button)
Change sort order to “Newest First”
Refresh the page (Ctrl+R or Cmd+R)
Verify token was created using CLI:
rspm list tokens
Revocation Doesn’t Work
If a token still works after revocation:
Verify revocation was successful (check status in UI)
Wait a few seconds for propagation
Check using CLI that token is revoked:
rspm list tokens --revokedContact server administrator if token still works after 1 minute
Security Best Practices
Token Creation
- Use descriptive names that include purpose and user
- Set expiration dates (default to 90 days or less)
- Grant minimum required scope
- Create separate tokens for each purpose
Token Storage
- Never commit tokens to version control
- Use environment variables or secrets management systems
- Share tokens securely (encrypted communication)
- Maintain a token inventory
Token Maintenance
- Review tokens monthly
- Rotate long-lived tokens quarterly
- Revoke orphaned tokens annually
- Document token usage and rotation schedule
Incident Response
If a token is compromised:
- Immediately revoke the token
- Review server logs for suspicious activity
- Notify affected users and systems
- Create a replacement token
- Update systems with the new token
- Document the incident
CLI Comparison
The web interface and CLI provide similar functionality. Use the web interface for interactive token management and the CLI for automation and bulk operations.
| Feature | Web Interface | CLI |
|---|---|---|
| Create tokens | ✅ Visual form | ✅ rspm create token |
| List tokens | ✅ Sortable table | ✅ rspm list tokens |
| View details | ✅ Modal | ✅ Verbose output |
| Revoke tokens | ✅ One-click | ✅ rspm revoke token |
| Filter by status | ✅ Built-in | ✅ Flags |
| Search tokens | ✅ Real-time | ❌ Use grep |
| Batch operations | ❌ | ✅ Scripts |
See Token Authentication for CLI commands and examples.